AWS Control Tower + SSO Landing Zone – Secure Multi-Account Cloud Governance
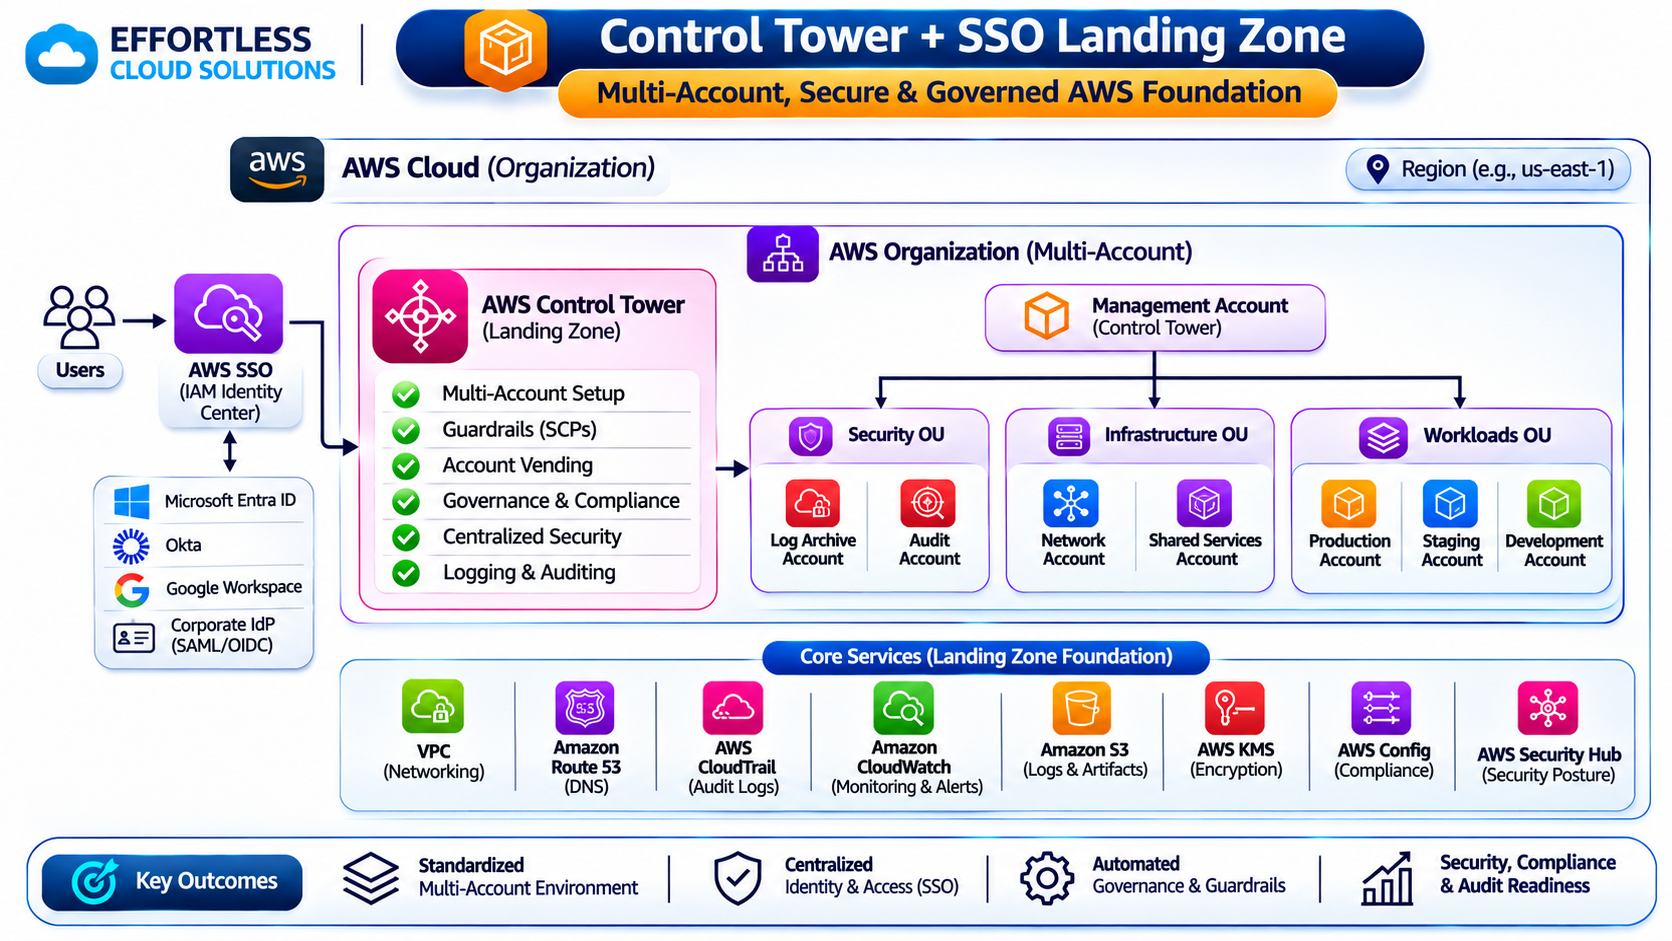
AWS Control Tower sets up and governs a secure, well-architected multi-account AWS environment. It creates a landing zone with centralized logging, security auditing, and identity management, applies preventive, detective, and proactive controls across every account, and provisions new accounts that are compliant from the moment they are created, so teams can move quickly without losing governance.
Benefits
uptime, backed by multi-AZ task placement and ECS automated recovery
faster deployment speed with automated blue/green pipelines
improvement in engineering team efficiency on AWS Fargate
A best-practice multi-account foundation built in hours instead of weeks of manual work
New, pre-configured accounts created on demand through Account Factory or Terraform
Preventive, detective, and proactive controls applied to whole organizational units at once
CloudTrail and AWS Config logs from every account delivered to a locked-down Log Archive account
Single sign-on to every account with role-based permission sets through IAM Identity Center
Changes that break the landing zone or its controls are detected and reported automatically
Overview
Many organizations start on AWS with a single account, or a handful of accounts created by different teams at different times. Workloads for development, testing, and production share the same boundaries, IAM users and access keys are created by hand in each account, logging is inconsistent or missing, and nobody has a complete view of what is deployed where. As the environment grows, security reviews become slow, audits become painful, and every new account is set up differently from the last.
AWS Control Tower replaces this with a governed, multi-account landing zone. It uses AWS Organizations to structure accounts into organizational units (OUs), creates dedicated Log Archive and Audit accounts, centralizes AWS CloudTrail and AWS Config data, and connects workforce identities through AWS IAM Identity Center. Controls enforce security and compliance rules across every OU, Account Factory provisions new accounts that inherit those rules automatically, and a single dashboard shows the compliance status of the whole environment.
About AWS Control Tower
AWS Control Tower is a managed service for setting up and governing a secure, multi-account AWS environment based on AWS best practices. It orchestrates AWS Organizations, AWS IAM Identity Center, AWS CloudTrail, AWS Config, AWS Service Catalog, and Amazon S3 to build a landing zone, and provides a catalog of managed controls implemented as service control policies (SCPs), resource control policies (RCPs), AWS Config rules, and AWS CloudFormation hooks. Control Tower continuously checks the landing zone for drift and offers managed updates as new landing zone versions are released.
Opportunity: Moving Beyond Ungoverned AWS Accounts
When AWS accounts are created without a common foundation, every account is configured differently. Some have CloudTrail enabled and some do not, logs are stored in the same account they describe and can be deleted by anyone with administrator access, and there is no consistent baseline for networking, encryption, or allowed Regions. Security teams cannot answer basic questions, such as which accounts expose public resources, without checking each one by hand.
Access is equally fragmented. Engineers have separate IAM users and long-lived access keys in each account, permissions grow over time and are rarely reviewed, and removing a departing employee means finding and deleting credentials across many accounts. New projects wait days or weeks for an account because creating one is a manual, ticket-driven process.
Organizations in this position need a single, governed foundation where every account follows the same rules, logs cannot be tampered with, access is managed centrally, and new accounts can be created quickly without bypassing security.
The Solution
Organizational Unit and Account Design
Accounts are grouped into OUs that reflect how workloads are governed, such as a Security OU for the Log Archive and Audit accounts, an Infrastructure OU for shared networking and services, Workloads OUs with separate Development, Staging, and Production OUs, and a Sandbox OU for experimentation. Each OU receives the controls that match its risk level.
Landing Zone Deployment
Control Tower deploys the landing zone in the selected home Region and governed Regions. It creates the Log Archive and Audit accounts, enables an organization-wide CloudTrail trail and AWS Config recording in every enrolled account, and applies the mandatory controls that protect the landing zone resources themselves.
Centralized, Tamper-Resistant Logging
CloudTrail and AWS Config data from every account are delivered to Amazon S3 buckets in the Log Archive account, encrypted with AWS Key Management Service (AWS KMS) and protected by controls that prevent deletion or modification. Logs are retained according to configurable lifecycle policies for audit and investigation.
Preventive Controls
Service control policies and resource control policies block actions that should never happen, regardless of the permissions granted inside an account. Examples include preventing CloudTrail or AWS Config from being disabled, denying the use of AWS Regions outside the approved list, blocking changes to landing zone resources, and preventing public access to Amazon S3 buckets.
Detective Controls
AWS Config rules managed by Control Tower continuously evaluate resources in every enrolled account, such as unencrypted storage, security groups open to the internet, or root user access keys. Noncompliant resources are reported on the Control Tower dashboard and sent as notifications to the Audit account, with integration into AWS Security Hub for a consolidated view.
Proactive Controls
AWS CloudFormation hooks check resources before they are created. Templates that would deploy noncompliant resources, such as unencrypted databases or load balancers without access logging, are stopped at deployment time instead of being discovered and fixed afterwards.
Centralized Identity with IAM Identity Center
AWS IAM Identity Center provides single sign-on to every account, connected to an existing identity provider such as Microsoft Entra ID, Okta, or Google Workspace. Permission sets, such as read-only, developer, and administrator, are assigned to groups per account, so access is granted and removed in one place and long-lived IAM user credentials are no longer needed.
Automated Account Provisioning
New accounts are created through Account Factory in the Control Tower console or AWS Service Catalog, or as code with Account Factory for Terraform (AFT). Each account is placed in the correct OU and inherits its controls immediately. Account Factory Customization blueprints and Customizations for AWS Control Tower apply standard baselines, such as VPC configuration, IAM roles, and budgets, to every new account automatically.
Enrolling Existing Accounts
Existing AWS accounts are brought under governance by moving them into a registered OU or enrolling them individually. Control Tower deploys its baseline resources into each account, and the OU's controls are applied, so legacy accounts reach the same standard as new ones.
Drift Detection and Landing Zone Updates
Control Tower detects drift, such as an account moved outside a registered OU or a modified control policy, and reports it for repair. When AWS releases a new landing zone version, the environment is updated through a managed process, and lifecycle events are published to Amazon EventBridge for automation.
Results
A Consistent Foundation for Every Account
Every account starts from the same baseline for logging, controls, and access, removing the configuration differences that come from manual setup.
Faster Account Delivery
Teams receive new, compliant accounts in minutes through Account Factory or a Terraform pull request, instead of waiting on a manual, ticket-driven process.
Guardrails That Cannot Be Bypassed
Preventive controls apply at the organization level, so even account administrators cannot disable logging, use unapproved Regions, or alter landing zone resources.
Audit-Ready Logging
An organization-wide, tamper-resistant record of API activity and resource configuration is stored in the Log Archive account and available for audits and investigations.
Simpler, Safer Access
Engineers sign in once through IAM Identity Center with temporary credentials, and access is granted or revoked centrally across all accounts.
Continuous Compliance Visibility
The Control Tower dashboard and Audit account notifications show noncompliant resources and drift across the environment as they happen, instead of during periodic reviews.
Room to Grow
New teams, projects, and environments are added as new accounts in the right OU, with governance applied automatically, so the environment scales without adding security overhead.
AWS Services Used
Core AWS building blocks powering high availability, elastic scaling, security, and automated deployments.
AWS Control Tower
Orchestrates multiple AWS services to deploy and govern an automated, multi-account landing zone with continuous compliance guardrails.
AWS Organizations
Provides central management and programmatic provisioning of AWS accounts into structured Organizational Units (OUs) with consolidated billing.
Service Control Policies (SCPs)
Organization-level guardrails that define the maximum available permissions for member accounts and OUs, impossible for account admins to override.
AWS IAM Identity Center
Centralized workforce authentication and single sign-on across all AWS accounts, integrating natively with Entra ID, Okta, and Google Workspace.
AWS CloudTrail
Continuously records and aggregates management and data plane API calls across all accounts into an immutable S3 bucket in the Log Archive account.
AWS Config
Assesses, audits, and evaluates resource configurations across the entire organization, flagging non-compliant infrastructure in real time.
AWS CloudFormation Hooks
Validates infrastructure declarations proactively before CloudFormation provisions resources, blocking non-compliant stacks before creation.
Amazon S3
Provides highly durable, secure object storage for centralized CloudTrail, Config, and VPC flow logs with S3 Object Lock and lifecycle tiering.
AWS KMS
Customer managed keys providing strict envelope encryption for centralized log archives, parameter stores, and cross-account data flows.
AWS Service Catalog
Standardizes pre-approved cloud services and enables self-service account provisioning with enforced baseline configurations.
Account Factory for Terraform (AFT)
Automates the creation and customization of AWS accounts using Terraform pipelines, keeping landing zone baselines under Git version control.
AWS Security Hub
Aggregates and prioritizes security findings from AWS services across member accounts into an organizational single pane of glass.
Amazon EventBridge & SNS
Captures Control Tower lifecycle events and triggers real-time security alerts and automated remediation workflows.
Send Us a Message
Ready to bring your ideas to life? Tell us about your project and our team will get back to you within one business day.
Denver, CO 80231